
Protecto Vault finds sensitive data, replaces it with tokens your AI can still work with, and returns real values only to authorized users. Deploy in private cloud, on-premises or air-gapped.
Live enterprise tenants at Automation Anywhere
Long texts processed per day at a SaaS company
Records protected at a healthcare insurer
A claims team wants an assistant over its support notes. Security strips every name first, so the model reads “[REDACTED] called about [REDACTED]’s claim” and loses track of who is who.
Answers get vague. The team turns masking off to ship, and the exposure comes back. Protecto Vault is built so you do not have to pick one.
When every name becomes the same placeholder, the model can no longer tell people, accounts or events apart.
One customer becomes several values, so joins break and the same person looks like three across your tools.
Support and fraud teams sometimes need the real value. Without a control, nobody can show who saw what, or why.
Step through the path with Protecto on and off, and see where real values end up. Vault is the foundation of the Protecto data control plane.
Synthetic example. Your policy decides what gets masked and who can see it.
Tables need tokens that fit the column. Free text needs tokens that keep the sentence readable. Protecto Vault applies the right strategy for structured and unstructured sources.
Consistent everywhere. “Sarah Mitchell” in your CRM, data warehouse, EHR or chat log maps to one token, so joins and foreign keys still work.
Accuracy you can measure. We track how well LLM answers hold up after masking with RARI, our accuracy metric.
Database columns
The masked value keeps the same length and character set, so it still passes downstream validation.
Text the model reads
Maya Shah called about claim CLM-88291 after her asthma follow-up.
<PERSON>0AmY 0AcJ</PERSON> called about claim <CLAIM_ID>Bicnh</CLAIM_ID> after her asthma follow-up.
The sentence and the entity types stay in place, so LLMs can still follow who did what.
Values held for security
Tokens come from system-level noise, not a predictable algorithm. They cannot be reversed without authorized vault access.
Synthetic examples. The same value always gets the same token, in any session, at any time.
You do not need to rebuild data protection for each AI project. Protecto Vault is a headless API, so one call from your code protects the data.
Request
PUT /api/vault/mask
{"mask": [{"value": "maya.shah@example.com"}]}
Response: token_value
<EMAIL>kAywW@ueS8y</EMAIL>
Synthetic example. Send the same email with the same token type from any job and you get the same token back.
Real-time, async and bulk APIs, from LangChain, LlamaIndex or your own code.
Use the API, a Snowflake UDF, Databricks, Kafka or Spark.
Protecto Vault is a headless API, so you can build it into your own auth, identity and access systems.
SaaS, private cloud, on-premises or air-gapped.
A SaaS company cut cost by 90% compared with its in-house estimate, and a Fortune 100 company deployed within days. Book a demo to start your free trial, which includes a 4-week pilot.
A sales agent and a support agent can read the same note, yet need different parts of it. CBAC decides at each request: who asks, for what task, and what they may see.
User access is not task access. Protecto Vault protects the values, and CBAC adds the control over when an agent or workflow can see them.
Example: the same account note read by three agents and one tool call, no schema, no fixed fields.
Raw note before any policy runs. Every entity is visible.
→ This is what enters the model before CBAC evaluates the request.
Healthcare has MRNs and NPI numbers. Banking has IBAN codes and internal policy fields. Generic tools miss them.
DeepSight, the agentic detection and classification engine inside Protecto Vault, reads the context and finds them.
Tokens are one part. Protecto also applies your policy, isolates each tenant and keeps the records your auditors ask for.
Each policy sets which entities are masked and how, then applies wherever Protecto runs.
Isolate teams and customers, with policy and retention set per tenant.
Every scan, mask and unmask is logged. Reports show where sensitive data flows and how your data policies were enforced.
Control the data lifecycle through the API.
Protecto handles the data protection. Your team focuses on building.
Feed your LLMs and agents without sending raw PII to external models. Protecto masks the data first and unmasks responses for authorized users only.
De-identify PHI across EHR exports, clinical notes and imaging metadata. Support HIPAA Safe Harbor de-identification while keeping model accuracy.
Tokenize PII and PCI data for fraud detection and credit risk models. Join customer data across systems without exposing raw values.
Give engineers masked copies of production data that keep their shape, so tests stay meaningful.
Mask large tables in bulk during data lake migrations, cloud moves or platform consolidations. Schema stays intact.
Share data across teams, subsidiaries and partners in different regions. The same record gets the same token everywhere.
| Entity | Protecto | AWS Comprehend | MS Presidio |
|---|---|---|---|
| SSN Identification | 100% | 31% | 81% |
| Credit Card | 100% | 49% | 64% |
| Phone Number | 99% | 62% | 60% |
“Protecto enabled us to deliver data security, privacy, and compliance for our AI features at scale across 5,000+ enterprise clients, strengthening customer trust in our AI automation solutions.”
Saudi privacy and banking
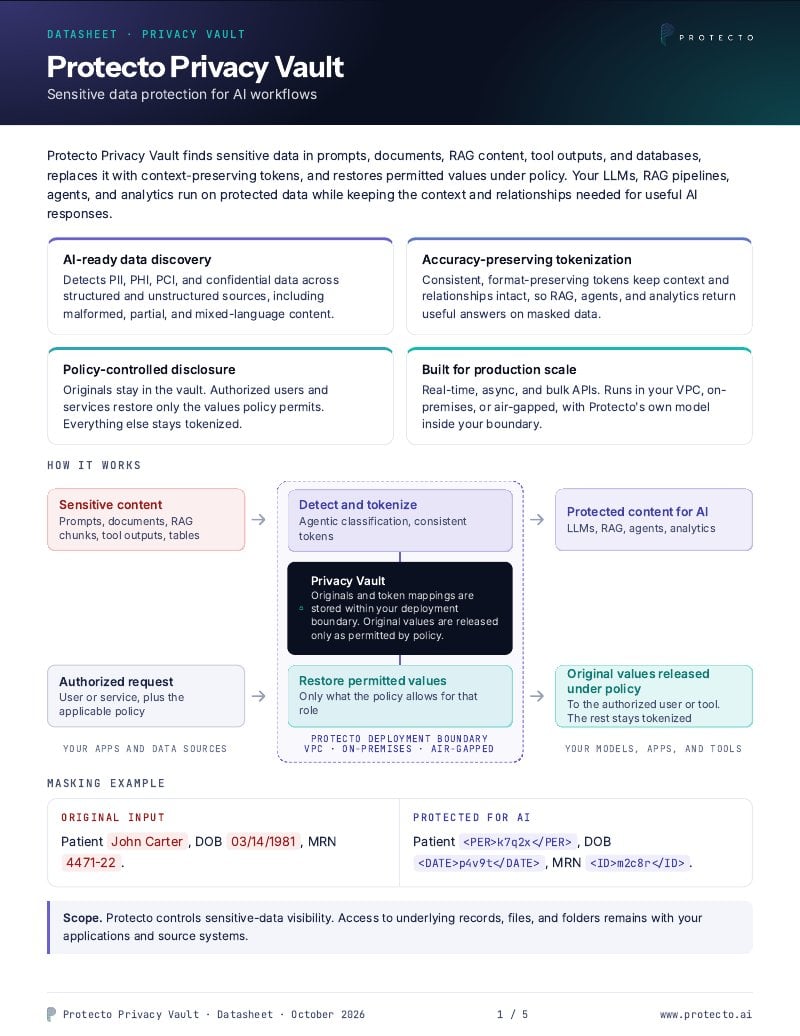
How to set a policy per destination for assistants, RAG, and agents, with a checklist for production.
A data privacy vault is a secure system that finds, masks, tokenizes and stores sensitive data such as PII, PHI, financial information and business-specific identifiers. It replaces that data with protected values and keeps the context applications and AI need. The original data can be restored only for authorized users and approved workflows.
Check detection accuracy, support for structured and unstructured data, consistent and reversible tokenization, granular access controls, audit logging, deployment flexibility, compliance support and performance at production scale.
Protecto Vault is a headless API. Your application calls it where sensitive data flows, you set detection and masking policies, and you define who can unmask. It runs in real time or asynchronously, as SaaS, in your private cloud, on-premises or air-gapped.
Yes, through Privacy Gateway. You keep each user’s masking and unmasking access in AD or Okta groups, and Gateway issues a Protecto auth key with that access at login. If you use Protecto Vault directly, it’s a headless API, so your team can build the integration around it.
It can. Placeholders that strip context leave the model guessing. Protecto keeps the semantic structure, so LLMs still understand what they are working with. We measure this with RARI, our accuracy metric.
The same value always gets the same token, in any session, at any time. So “Sarah J. Mitchell” in your CRM and data warehouse maps to one token, and you can join datasets and run analytics without raw PII.
Usually, yes. Tokenization is pseudonymization, not anonymization: while a mapping exists, a token can be linked back to a person. Your counsel decides what that means for each dataset.
Yes. DeepSight lets you add custom entity types, and they can be added in days. Industry-specific add-ons for healthcare and banking are also available.
SOC 2 Type II, ISO 27001, HIPAA, GDPR, PDPL, SAMA and CPRA. When Protecto hosts or manages the service, or has access to your installed instance, Protecto signs a BAA before PHI flows. When Protecto runs in your environment with no Protecto access, Protecto does not receive PHI and is not a business associate.
Bring a sample, with test data if you prefer. In 30 minutes, we will show you what Protecto finds and how your AI still works.
A third-party study compares how accurately Protecto, Microsoft Presidio, and AWS Comprehend find personal and health data in unstructured text.
By submitting you agree to Protecto’s privacy policy.
Features that safeguard your data across agents, AI applications, RAG pipelines, MCPs, data lakes, and enterprise systems.
By submitting you agree to Protecto’s privacy policy.
How DeepSight finds PII and PHI from context, with Protecto’s internal test results.
By submitting you agree to Protecto’s privacy policy.
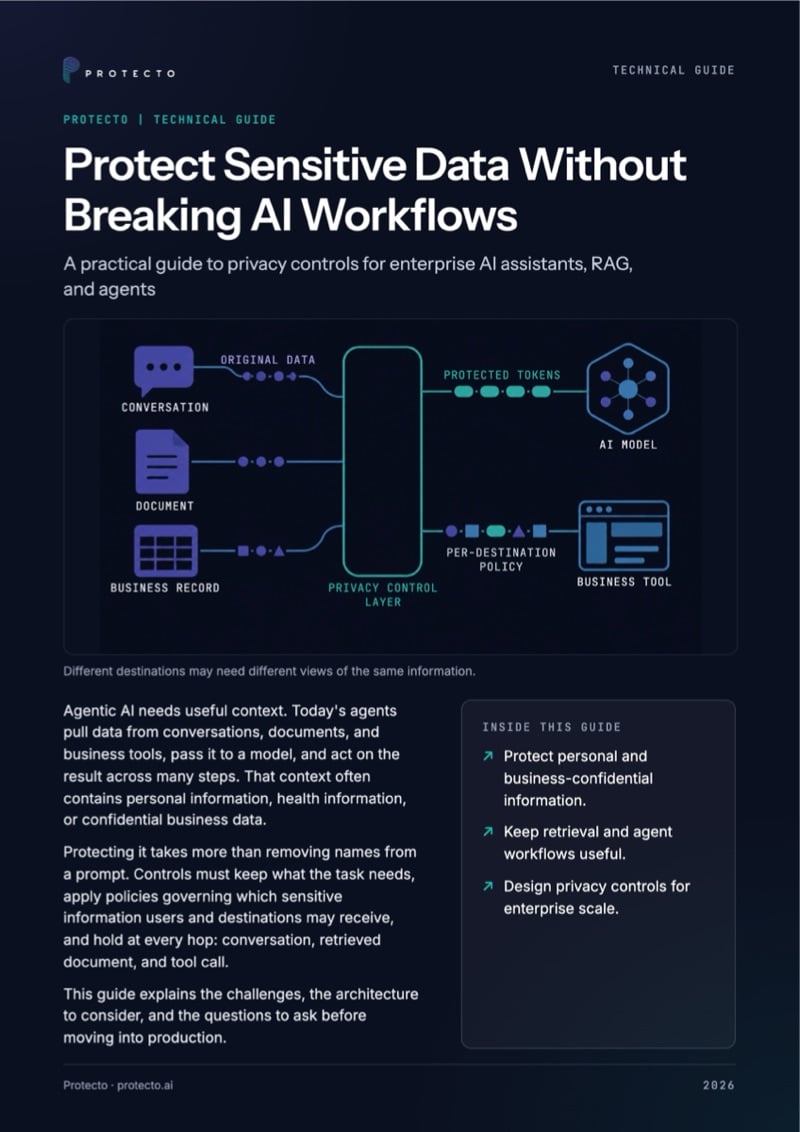
A practical guide to privacy controls for AI assistants, RAG, and agents. One workflow traced from request to CRM update, with what each destination may see.
By submitting you agree to Protecto’s privacy policy.